Mobile Security Research and Audit
Garbo allow teams to conduct comprehensive mobile security research and auditing by recreating, analyzing, and validating real-world vulnerabilities within isolated digital twin enviroments. It enables the reproduction of complex exploitation chains, forensic validation and also controlled malware detonation.
Example: Reproducing a real-world iOS vulnerability
In 2023, several zero-day vulnerabilities in iOS were exploited in the wild, later documented in Apple’s security advisories and analyzed by Citizen Lab. These incidents demonstrated how threat actors could compromise modern iPhones through zero-click exploits delivered via messaging services.
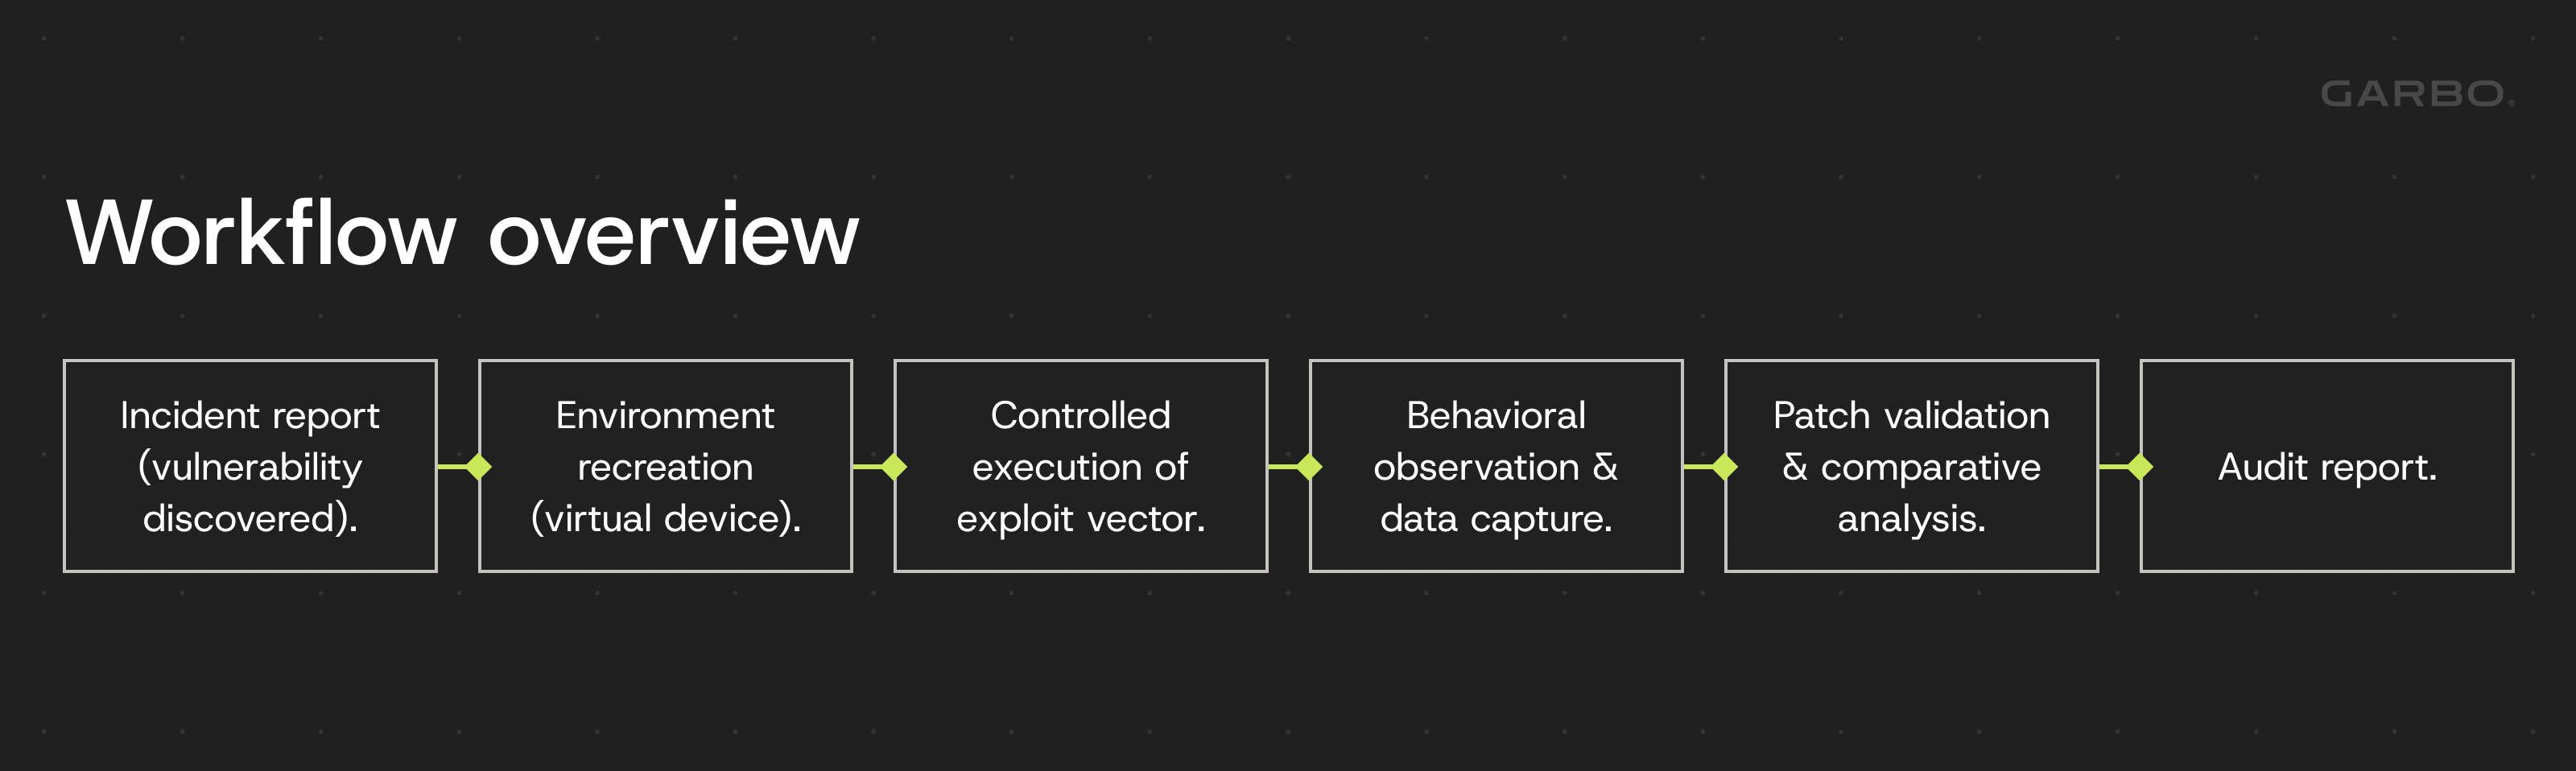
Using Garbo, a research or audit team could:
- Recreate the environment
- Deploy multiple virtual iPhones running iOS 16 and 17.
- Configure them with identical firmware and system settings as affected models.
- Reproduce and observe the behavior
- Execute payloads or network inputs under controlled conditions.
- Capture system responses and interactions.
- Monitor low-level processes, memory events, and I/O activity in real time.
- Validate patches and mitigations
- Apply vendor security updates to cloned devices.
- Compare pre- and post-patch behavior, confirming whether the vulnerability has been neutralized.
- Export audit-ready reports for internal or contractual compliance.